On 15 October 2026 the Australian Signals Directorate published Essentials, the successor to the Essential Eight. The Essential Eight has been Australia's baseline cyber security guidance since 2017. If a client, insurer or tender has ever asked you about "Maturity Level 1," that was the Essential Eight.
Here is what landed, who it is for, and what to do while the industry works out the details. The short version: it replaces the Essential Eight over the next two years, it is written for government and large organisations, and nobody can certify you against it.
What is ASD Essentials?
ASD Essentials is a set of guidance chapters, one per technology environment, that replaces the single Essential Eight checklist. ASD published three chapters on day one: enterprise IT, operational technology and cloud. Guidance for AI-enabled systems runs through all three.
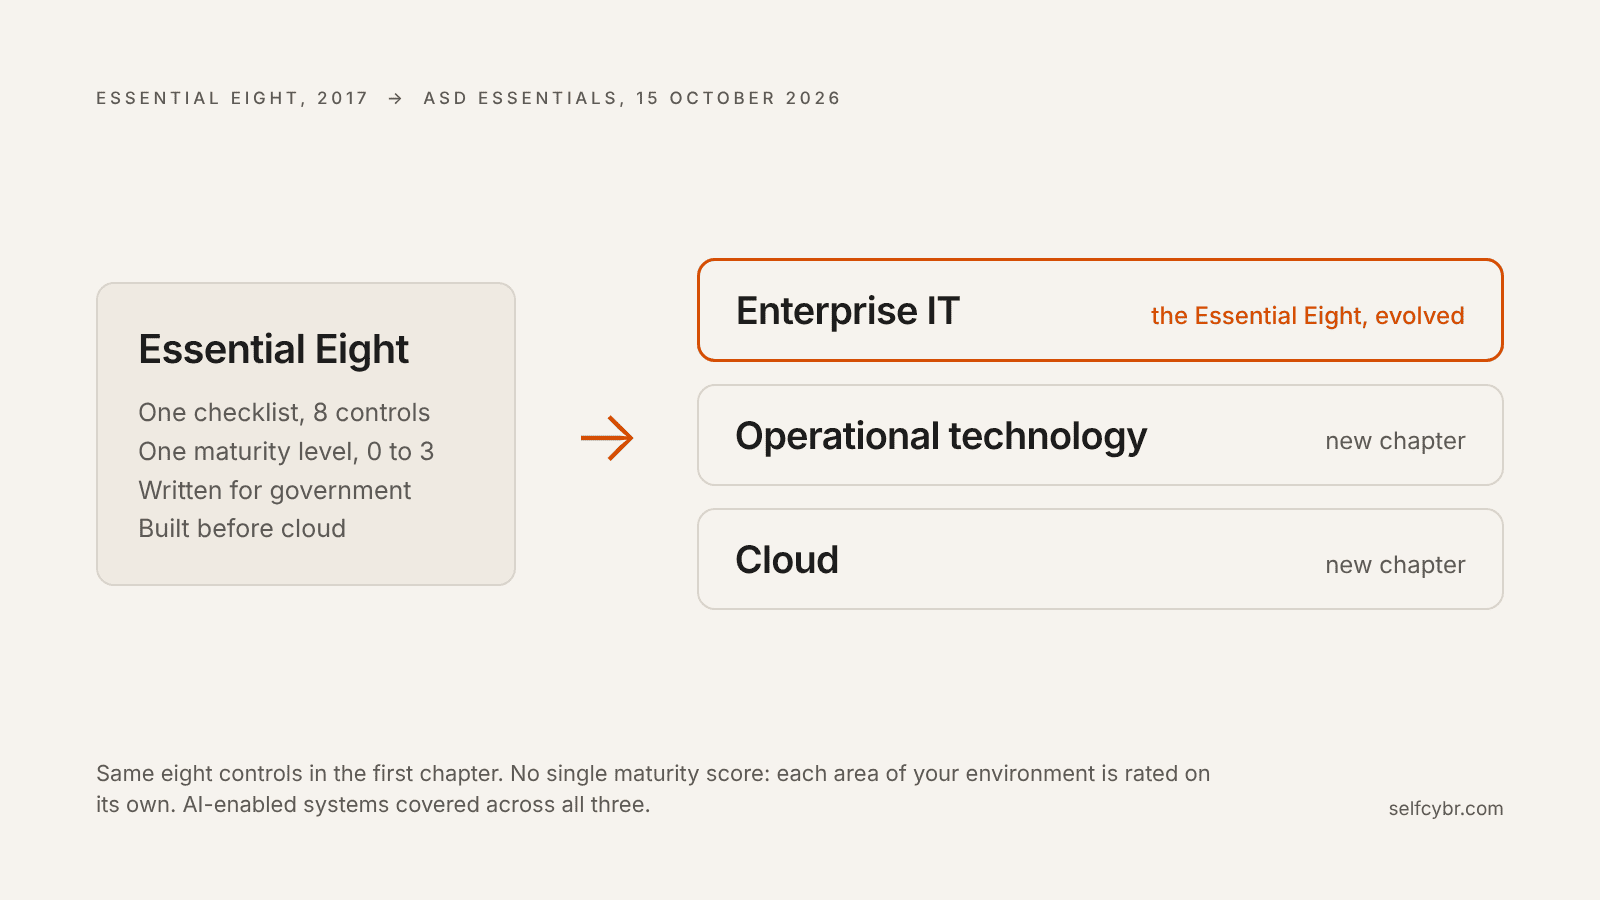
The enterprise IT chapter is the direct descendant of the Essential Eight. The same eight controls are still there: patching, multi-factor authentication, application control, restricted admin privileges, backups and the rest. What changes is how you are rated. The Essential Eight gave you one maturity level, 0 to 3. Essentials rates each area of your environment separately.
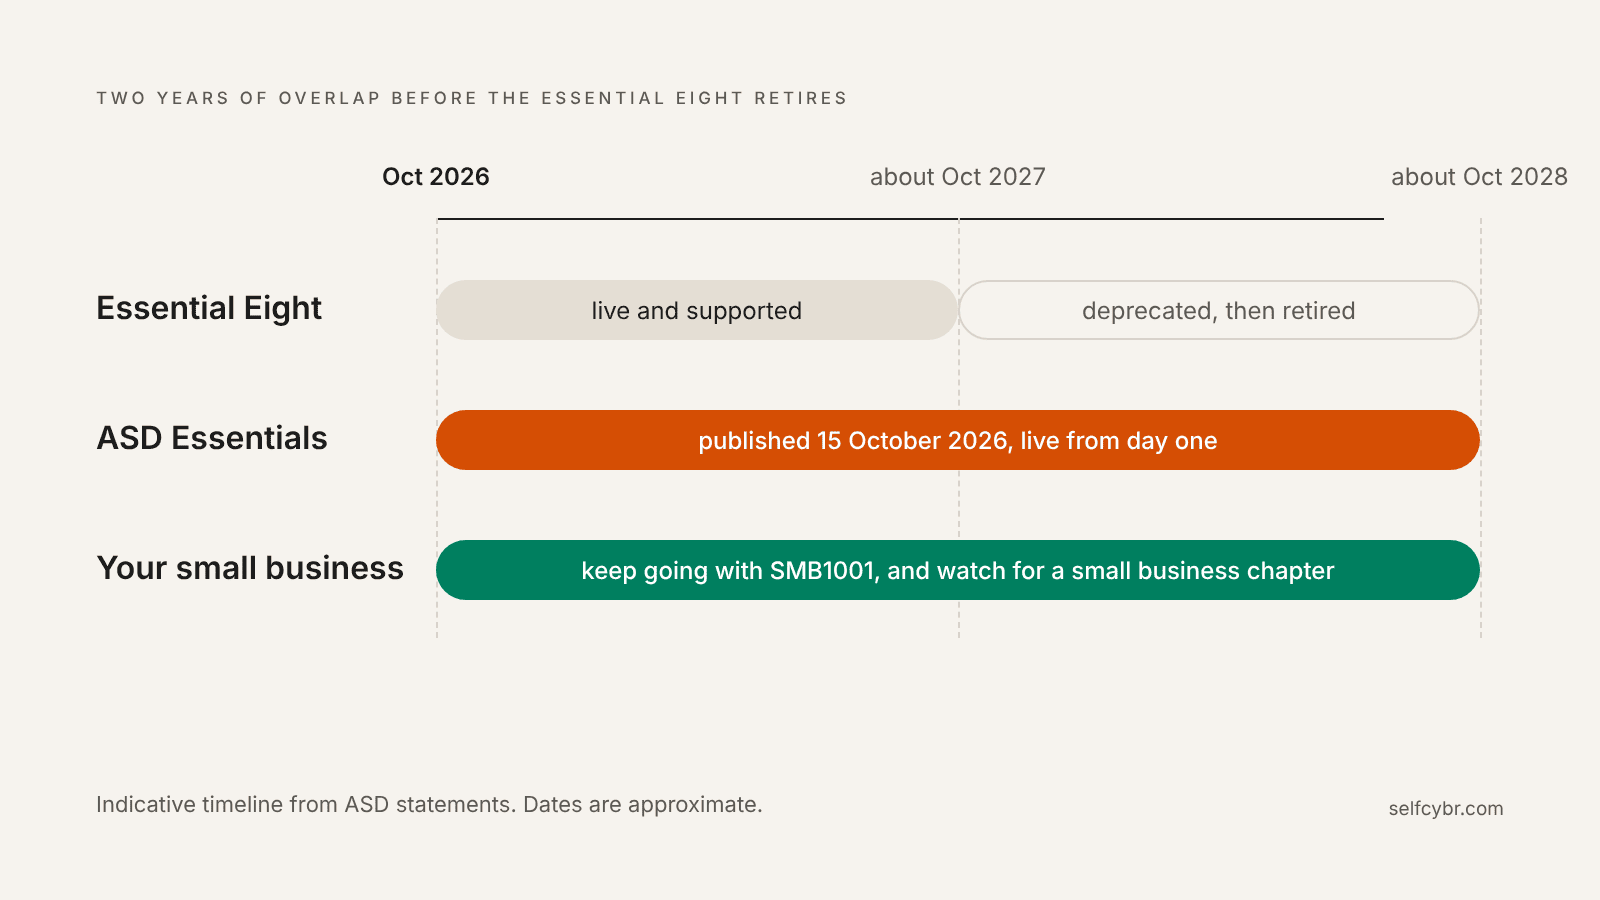
The Essential Eight is not switched off. ASD says both frameworks stay live during a transition of roughly two years, with the Essential Eight expected to be deprecated at about the 12-month mark and retired at about 24 months. Your regulatory obligations have not changed until your regulator says so.
Does ASD Essentials apply to my small business?
Not directly. ASD names its audience on the cover: government agencies, critical infrastructure operators and large organisations. There is no small business chapter, and nothing in the three published chapters is scaled for a business with five or fifty staff.
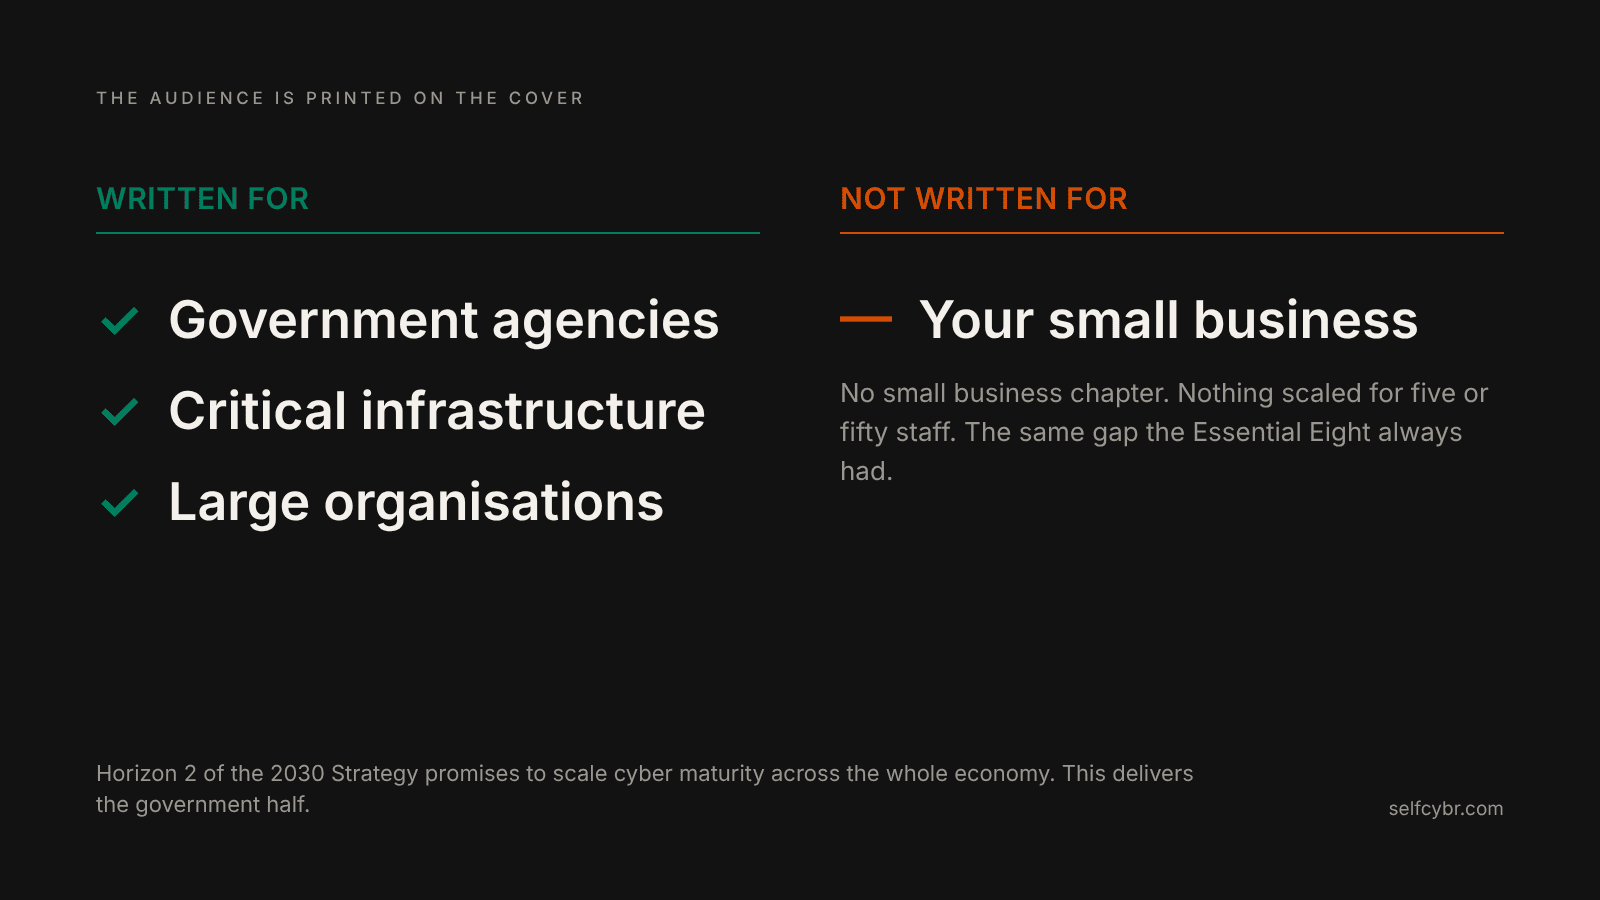
That is not a flaw in the framework. It is the same gap the Essential Eight always had. A 15-person firm with an outsourced IT provider was never going to reach Maturity Level 2 on a standard written for a department with its own security team. Commercial standards such as SMB1001 exist precisely because the government baseline skipped small business.
It matters more now because of where we are in the national strategy. The 2023-2030 Australian Cyber Security Strategy is in its second phase, Horizon 2 (2026 to 2028), whose stated goal is to scale cyber maturity across the whole economy, not just the regulated end of it. Essentials delivers the government and critical infrastructure half of that promise. A small business chapter is the piece that would make the rest of it true, and it is the one worth watching for.
Where it will reach you indirectly is through your customers. If you supply a government agency, a hospital, a utility or a large company, their security questionnaires will start referencing Essentials instead of the Essential Eight over the next year or two. Expect that in contracts before you see it anywhere else.
Can someone certify my business in ASD Essentials?
No. ASD does not certify businesses against the Essential Eight and has not set up any scheme for Essentials. Both are guidance, not standards with an accreditation body behind them. An assessor can test your controls and write a report. Nobody can issue you an ASD-recognised certificate, because none exists.
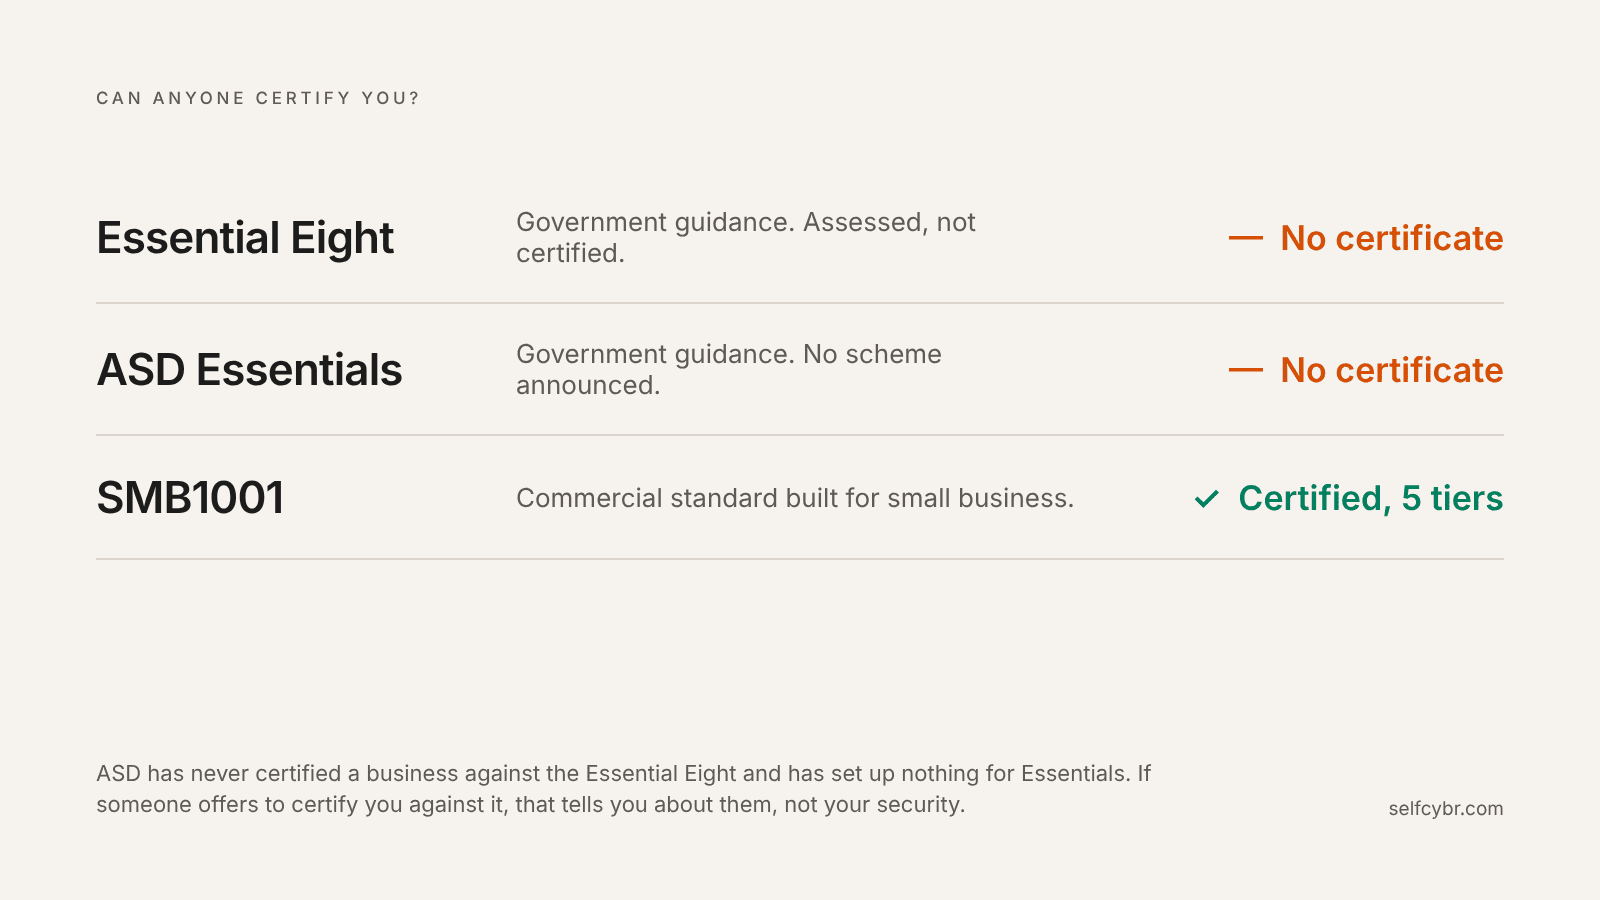
That has always been true of "Essential Eight certified" claims, and it will be true of "Essentials certified" claims when they start appearing in your inbox. If a provider offers to certify you against Essentials in the coming weeks, that tells you more about the provider than about your security.
What should I do right now?
Nothing about Essentials. That is our advice to every small business this month, and we say it as a company that makes its living helping businesses meet these standards. If you are partway through SMB1001, keep going. Nothing published today changes that path.
Here is why. Nobody has implemented Essentials yet, so there is no precedent to learn from and no track record of what assessors will accept. There is no product that makes you compliant overnight, whatever the sales emails over the next fortnight say. And your obligations have not changed. ASD has said organisations should keep meeting their existing regulatory requirements until their regulator announces otherwise.
Give the industry a few weeks to read the chapters properly and work out what they actually ask of a business your size. The people who rush at Essentials now will spend money on a framework they do not yet understand, written for organisations they do not resemble.
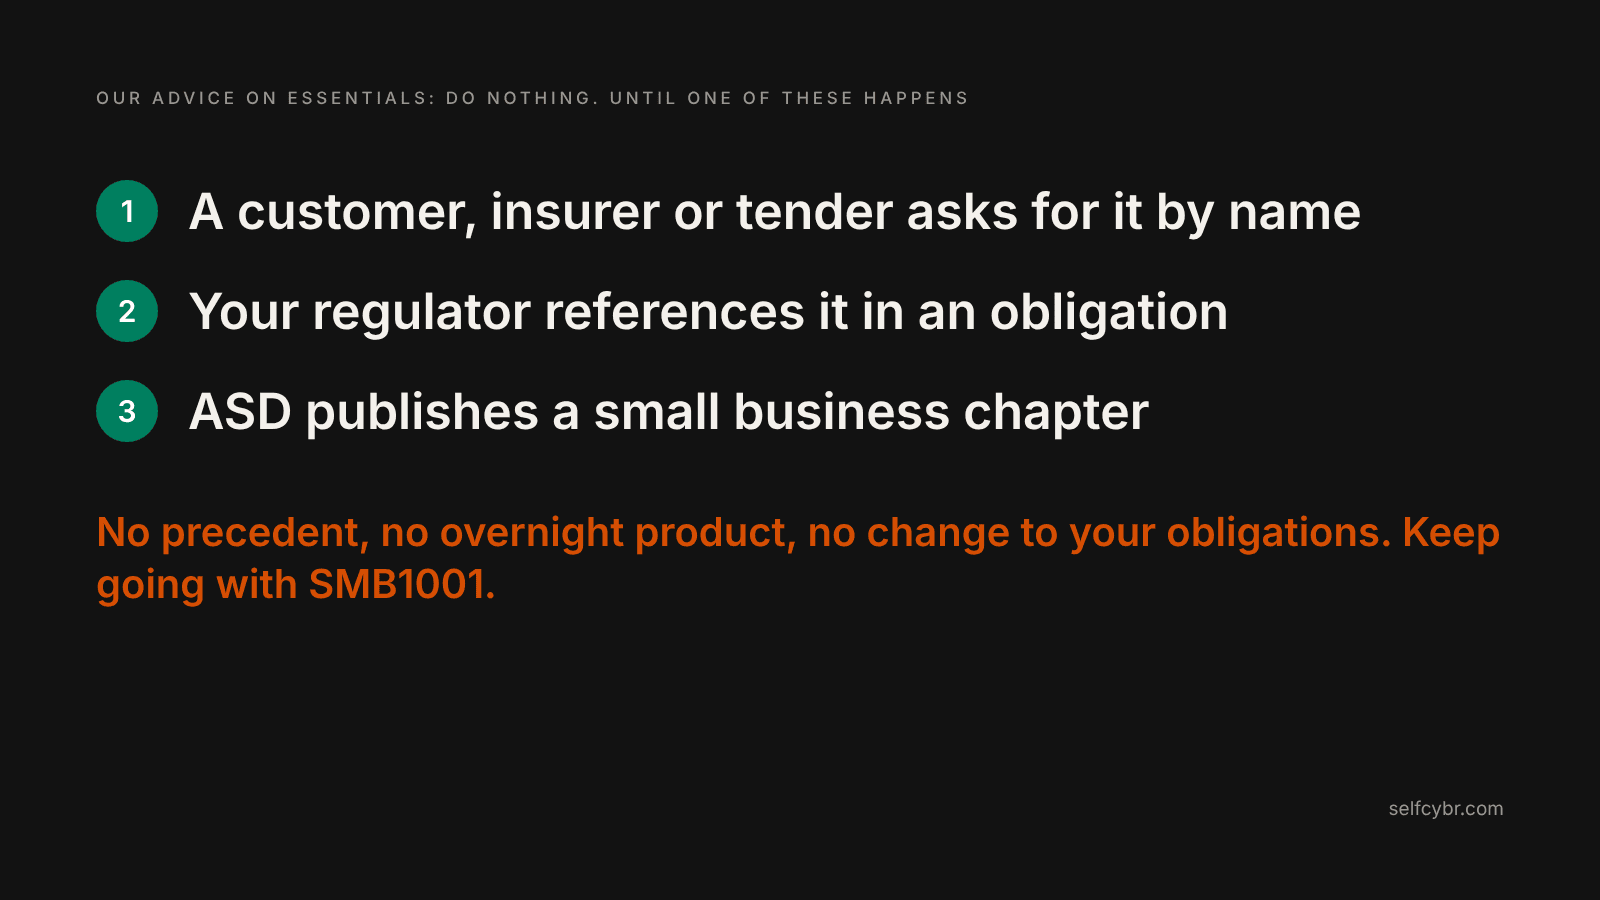
Until then, nothing about your obligations changes, and nothing you are doing today is wasted.
If you want to improve your security now
You are not short of options, and none of them are made redundant by Essentials.
| Framework | Built for | Ends in a certificate? | Best fit |
|---|---|---|---|
| SMB1001 | Small and medium business | Yes, five tiers from Bronze to Diamond | Most businesses under 50 staff. Clients and insurers recognise the badge. |
| ISO 27001 | Any size, management-system based | Yes, audited by an accredited body | Businesses selling into enterprise or overseas. |
| NIST CSF | Any size, risk-based | No | Structuring a security program without a compliance target. |
For most small businesses, SMB1001 is the right place to be, and the right place to stay. It is tiered so you can start at Bronze and climb, it is priced for businesses without an IT department, and the certificate is something a client can check. Keep implementing it, and keep an eye out for ASD publishing a small business chapter of Essentials. If that day comes, a business already certified against SMB1001 will be the best placed to map across.
Where SelfCybr fits
We help small businesses get certified in SMB1001, for one all-inclusive price and no lock-in contract. If we can't get you certification-ready, the final instalment isn't payable. We will add Essentials to that list when there is a sensible way to apply it to a business your size, and not before.
If you want to start now, our GRC as a Service page walks you through exactly what each standard covers and what it costs. If you would rather wait and watch, subscribe to The Feed and we will tell you when Essentials actually changes something for you.
Related reading
- What five AISA CyberCons taught me
- Two conferences, two worlds: DEF CON Singapore and Milipol TechX
- How to tell if an email is really from a company
Sources
ASD, Consultation on evolution of Essential Eight, 15 June 2026. Cyber Daily, Essential Eight Evolved: ASD launches ASD Essentials, 15 October 2026. Cyber Daily, ASD says it will retire the Essential Eight within next 2 years, June 2026. Department of Home Affairs, 2023-2030 Australian Cyber Security Strategy Horizon 2 Action Plan, 2026.